Secure your access.
Stay in control.
Vauban is a sovereign, self-hosted Privileged Access Management (PAM) and security bastion built in Rust for SSH, RDP, IACS and MCP access to critical infrastructure across enterprise, industrial, and defense environments.
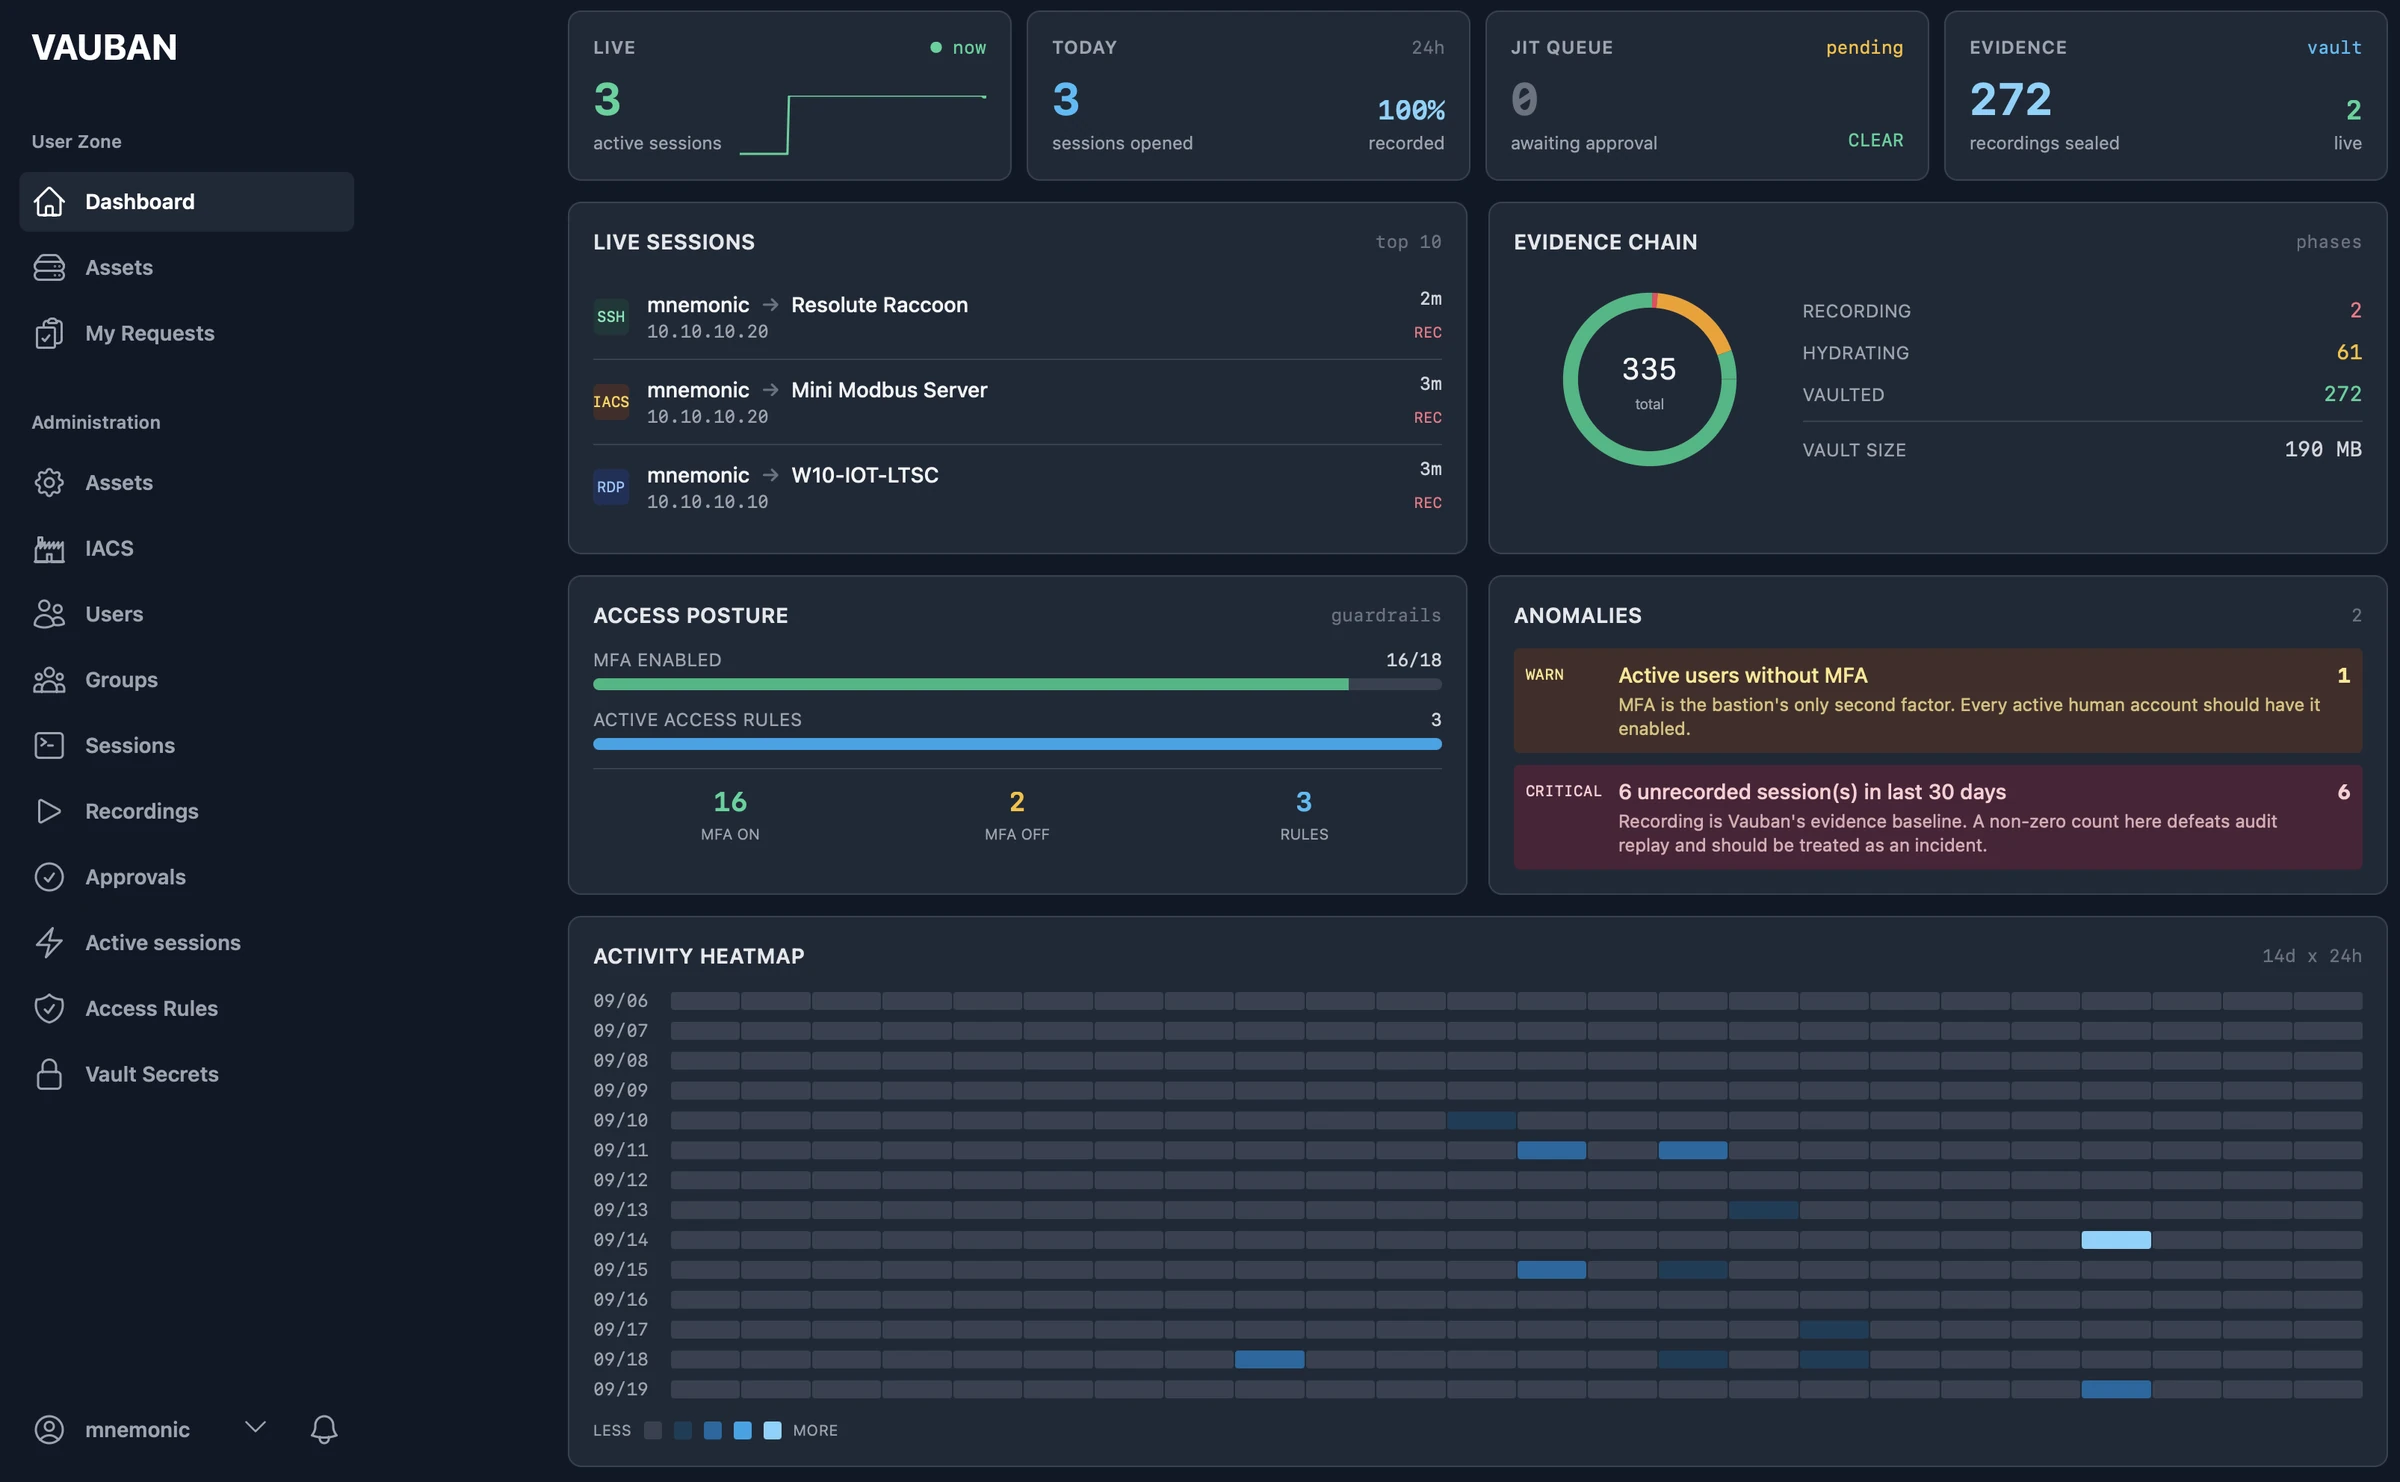
Everything a PAM should do
Secure access, full traceability, and granular control — with no proprietary vendor lock-in.
SSH, RDP & IACS Proxy
Access your Linux and Windows servers directly from the browser. SSH terminal in the browser, RDP remote desktop in the browser. Access your industrial controller with protocols recognition.
MFA Authentication
TOTP, HOTP, and SSO integration (OIDC, SAML). Compatible with LDAP and Active Directory to integrate with your existing directory.
Access Control
Granular policies by roles, groups, and assets groups through the access policy and access rules engine. Just-In-Time access to limit temporal exposure.
Session Recording
MP4 video recording with BLAKE3 cryptographic integrity. Replay any session for audit or investigation.
Real-Time Monitoring
Live dashboard: active sessions, metrics, security alerts, and recent activity.
Secrets Vault
Encrypted storage for SSH keys, passwords, and certificates. AES-GCM encryption with HKDF-SHA3 key derivation.
AI Agents Control
Control AI agent chains of actions, with stated intent and a reviewed execution plan. Instant revocation on drift, plus a contestation mechanism for operators.
Modular architecture
Ten isolated services, orchestrated by a single supervisor. OpenSSH-inspired privilege separation, Capsicum sandboxing.
vauban-web
Web interface, REST API, WebSocket
vauban-auth
MFA, SSO, LDAPS, Active Directory
vauban-access
Access policy and access rules engine
vauban-vault
Encrypted secrets management
vauban-proxy-ssh
Sandboxed SSH proxy
vauban-proxy-rdp
Sandboxed RDP proxy with H.264 video streaming
vauban-proxy-iacs
Sandboxed IACS proxy with industrial protocols recognition
vauban-proxy-mcp
Sandboxed MCP proxy
vauban-audit
Recording and storage
vauban-mailer
Sandboxed SMTP for notifications and alerts
Why Vauban
A sovereign approach to access security, with no compromises.
Open Source and Auditable
Source code available under BSD-2-Clause license. No black box: every line is verifiable by your teams or an independent auditor.
Full Sovereignty
Deployed on your infrastructure, under your control. No data flows through a third-party cloud.
Secure by Design
Rust eliminates memory vulnerabilities. Privilege separation and Capsicum sandboxing limit the impact of a compromise.
NIS2 Compliance
Full traceability, session recording with cryptographic integrity, and granular access control.
Vauban vs. proprietary solutions
Frequently asked questions
01 What is Privileged Access Management (PAM)? +
Privileged Access Management (PAM) secures, controls and audits privileged access to critical infrastructure. Vauban provides PAM capabilities including privileged session management, SSH, RDP and IACS proxying, MFA, RBAC, Just-In-Time access, secrets management, session recording and audit trails.
02 What is a security bastion? +
A bastion is a hardened intermediary server that controls and traces all access to your servers and network equipment. It acts as a single gateway between your teams and your infrastructure, eliminating unsupervised direct access.
03 What protocols are supported? +
SSH and RDP (with optimized H.264 encoding), plus IACS industrial protocols (Modbus TCP, OPC-UA, PROFINET, IEC 60870-5-104, EtherNet/IP, BACnet/SC, DNP3, IEC 61850 MMS) via sandboxed EWS tunneling. SSH connections are accessible through a virtual terminal in the browser, and RDP sessions through video streaming for native rendering with no plugin and no thick client required.
04 What is Capsicum sandboxing? +
Capsicum is a confinement mechanism developed with funding from DARPA (U.S. Department of Defense). It restricts each process's capabilities to the bare minimum required, drastically limiting the impact of a potential compromise.
05 How does Vauban help with NIS2 compliance? +
NIS2 requires access traceability and audit capabilities for essential and important entities. Vauban records every session with cryptographic integrity (BLAKE3), enforces RBAC access control, and provides detailed audit logs.
06 How much does Vauban cost? +
Vauban is free and open source under the BSD-2-Clause license. You can use, modify, and redistribute it freely. Subscriptions are available for priority security fix notifications, 5-year LTS (long-term support) release cycles, certified builds, and priority bug resolution. Integration services and professional support are also available on request, along with Vauban-qualified hardware (hardware appliance).